
Security by Design in digital products
8 October 2025 · 3 min read
The Cyber Resilience Act turns Security by Design from good practice into a requirement for manufacturers. The article links the essential requirements in Annex I of the CRA with the four NIST SSDF practice groups and identifies the obligation that has applied since 11 September 2026.

Regulation (EU) 2024/2847, the Cyber Resilience Act (CRA), covers products with digital elements made available on the EU market. It generally applies from 11 December 2027, but the reporting obligations of manufacturers under Article 14 have applied since 11 September 2026 (Article 71(2)).
For a product team this means that secure development practices must leave a trace: a decision on the default configuration, a record of vulnerability handling and a description of the update path. The article sets the CRA requirements against the NIST SSDF framework, which can be introduced into an existing development process.
In this article
Product requirements in Annex I
Part I of Annex I to the CRA starts from the principle that a product is designed, developed and produced to ensure a level of cybersecurity appropriate to the risks. On the basis of the risk assessment and where applicable, the product:
- is made available without known exploitable vulnerabilities,
- has a secure by default configuration, including the possibility to reset it to its original state,
- allows vulnerabilities to be addressed through security updates, automatic where applicable, with an opt-out,
- protects against unauthorised access through authentication, identity and access management,
- protects the confidentiality and integrity of data, among others by encryption,
- processes only the data necessary for its intended purpose,
- protects the availability of essential functions, including after an incident and against denial-of-service attacks.
Each point calls for a design decision and evidence in the technical documentation (author’s analysis).
The four NIST SSDF practice groups
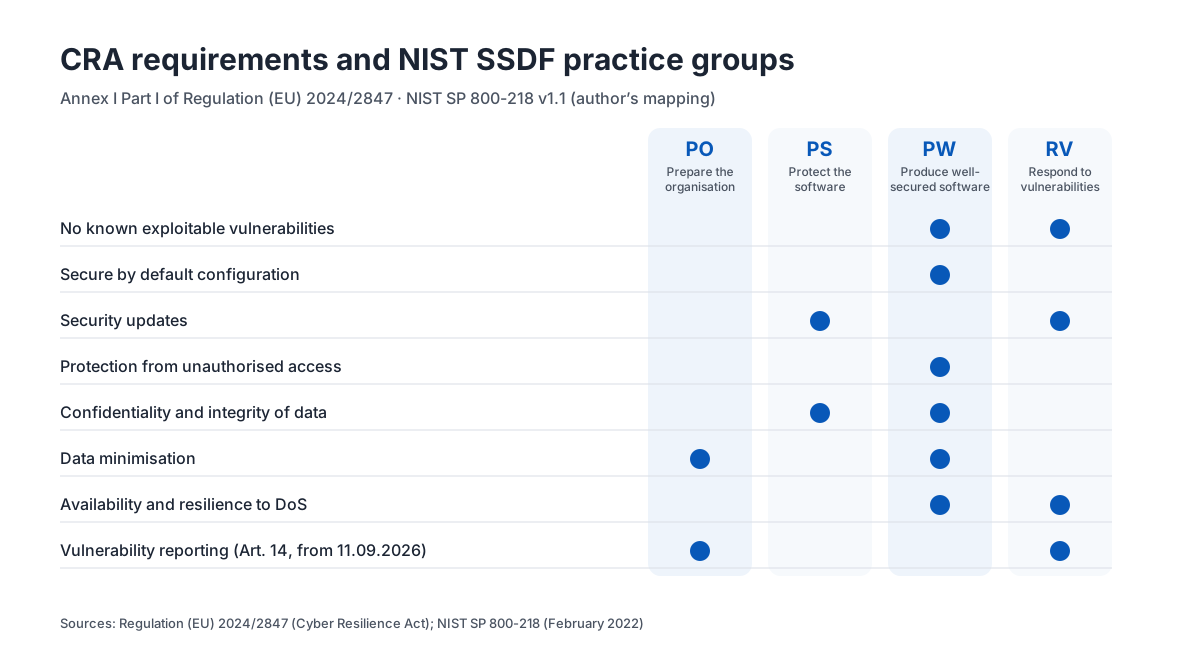
The Secure Software Development Framework is set out in NIST SP 800-218, version 1.1 of February 2022. Its practices fall into four groups. Prepare the Organization (PO) covers the people, processes and technology needed for secure development. Protect the Software (PS) concerns protecting all components from tampering and unauthorised access. Produce Well-Secured Software (PW) aims to minimise vulnerabilities in releases. Respond to Vulnerabilities (RV) covers finding residual vulnerabilities in releases and preventing similar ones in the future.
Mapping the CRA requirements to these groups shows that most product obligations rest on PW practices, while updates and vulnerability reporting rest on RV practices (author’s analysis).
Vulnerability reporting from 11 September 2026
Since 11 September 2026 a manufacturer notifies any actively exploited vulnerability in its product that it becomes aware of to the CSIRT designated as coordinator and to ENISA, through the single reporting platform (Article 14(1)). An early warning is due without undue delay and in any event within 24 hours of the manufacturer becoming aware of the vulnerability. A vulnerability notification with general information about the product, the nature of the exploit and the measures taken follows within 72 hours (Article 14(2)).
Deadlines measured in hours require an established point of contact, a register of reports with the time of receipt and an assigned person who assesses whether a vulnerability is actively exploited (author’s analysis).
Sources
- Regulation (EU) 2024/2847 of the European Parliament and of the Council of 23 October 2024 on horizontal cybersecurity requirements for products with digital elements (Cyber Resilience Act) – eur-lex.europa.eu/eli/reg/2024/2847/oj
- NIST SP 800-218, Secure Software Development Framework (SSDF) Version 1.1, February 2022 – csrc.nist.gov/pubs/sp/800/218/final
Key takeaways
- The Cyber Resilience Act generally applies from 11 December 2027, but the reporting obligation in Article 14 has applied since 11 September 2026.
- The Annex I requirements concern product properties, so they require design decisions and evidence in the technical documentation.
- The NIST SSDF practice groups help organise CRA compliance within an existing development process.
- Reporting an actively exploited vulnerability within 24 and 72 hours requires a report register and a designated owner.
Next steps
- Identifying which products with digital elements are made available on the EU market and fall under the CRA.
- Documenting the default configuration of each product and how to reset it to its original state.
- Designating a point of contact and a vulnerability assessment procedure that records the time of receipt.
- Assigning PO, PS, PW and RV practices to stages of the development process and to owners.