
NIS2 in IT system architecture
20 January 2026 · 4 min read
The NIS2 Directive and the amended Polish National Cybersecurity System Act translate into design decisions. The article maps the ten measures listed in Article 21(2) of the Directive to system components and describes the incident reporting deadlines in force in Poland since 3 April 2026.

Directive (EU) 2022/2555, known as NIS2, requires essential and important entities to take cybersecurity risk-management measures, to have them overseen by their management bodies and to report significant incidents. In Poland it is transposed by the Act of 23 January 2026 amending the National Cybersecurity System Act (Journal of Laws 2026 item 252), in force since 3 April 2026.
The rules define the required outcome and leave the choice of technology to the entity. The article links the requirements to elements that a project team plans, builds and documents in the architecture: from the asset register to recording when an incident was detected.
In this article
Scope and deadlines in Poland
Member States have applied the measures transposing NIS2 since 18 October 2024 (Article 41(1) of the Directive). The Polish amendment to the National Cybersecurity System Act (the KSC Act) has applied since 3 April 2026.
Entities that met the criteria for an essential or important entity on the day the amendment entered into force must meet the obligations in Chapter 3 of the Act within 12 months (Article 33(1) of the amending act), that is by 3 April 2027 (author’s calculation). Essential entities carry out their first audit within 24 months (Article 33(2)). The schedule for applications to the register of essential and important entities is set in a notice issued by the minister responsible for digital affairs (Article 34(3)). Financial penalties under the Act may first be imposed two years after the amendment entered into force (Article 35).
Article 21(2) measures in system components
Article 21(2) of the Directive lists at least ten risk-management elements, from risk analysis policies to multi-factor authentication. Each has a counterpart in the system architecture and its documentation. The mapping below is the author’s analysis.
- Risk analysis (point a) – an asset register with an owner and a risk assessment for each component.
- Incident handling (point b) – a central event log, alert rules and a reporting procedure.
- Business continuity (point c) – backups with a documented restore test.
- Supply chain (point d) – a supplier register and security requirements in contracts.
- Acquisition, development and maintenance (point e) – a development process covering vulnerability handling and disclosure.
- Effectiveness assessment (point f) – reviews, tests and indicators with recorded results.
- Cyber hygiene and training (point g) – a training plan with attendance records as evidence.
- Cryptography (point h) – encryption of data in transit and at rest, key management.
- Human resources, access control and assets (point i) – roles, least privilege and periodic account reviews.
- Multi-factor authentication and secured communications (point j) – MFA for administrative accounts and a fallback communication channel.
Incident reporting in system practice
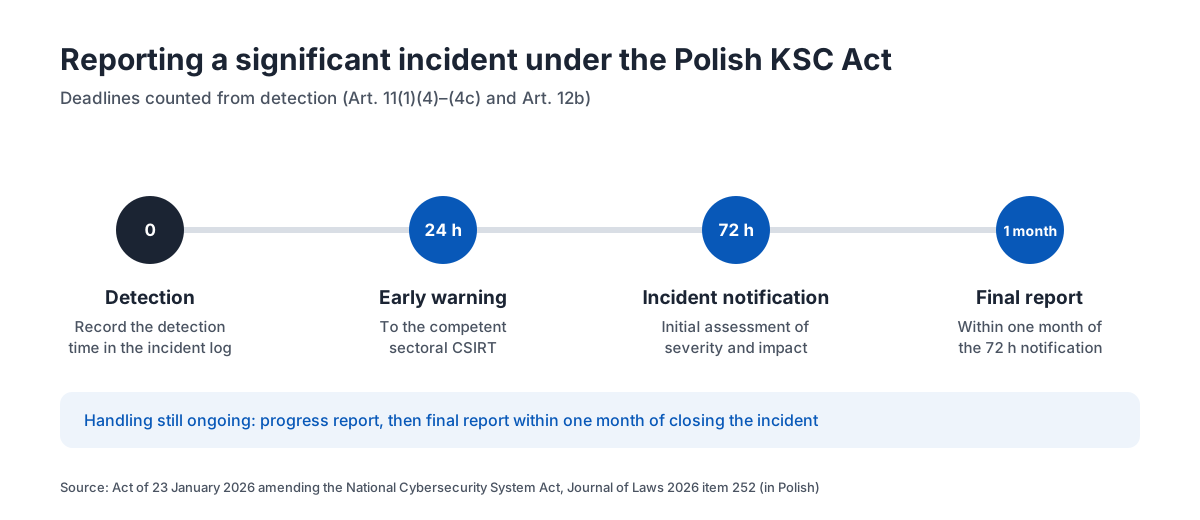
The Directive counts deadlines from becoming aware of a significant incident (Article 23(4)). The Polish Act counts them from the moment the incident is detected. An early warning goes to the competent sectoral CSIRT within 24 hours, the incident notification within 72 hours, and the final report no later than one month after the notification (Article 11(1)(4)–(4c)). If incident handling is still ongoing, the entity submits a progress report and then the final report within one month of closing the incident (Article 12b).
This gives the system one concrete requirement: the incident log should store the detection time as a separate field and calculate the following deadlines from it (author’s analysis).
Accountability of the management body
The management body of an essential or important entity approves the risk-management measures, oversees their implementation and can be held liable for infringements (Article 20(1) of the Directive). Its members follow regular training to identify risks and assess risk-management practices (Article 20(2)).
In a system this becomes a management report: the state of the risk register, restore test results and the number of incidents in the period, with the date and the approver (author’s analysis).
Sources
- Directive (EU) 2022/2555 of the European Parliament and of the Council of 14 December 2022 (NIS2), OJ L 333, 27.12.2022, p. 80 – eur-lex.europa.eu/eli/dir/2022/2555/oj
- Act of 23 January 2026 amending the National Cybersecurity System Act and certain other acts, Journal of Laws 2026 item 252 – isap.sejm.gov.pl (WDU20260000252) (in Polish)
Key takeaways
- The measures in Article 21(2) of NIS2 can be assigned to specific system components, which keeps compliance documentation in order.
- The Polish Act counts reporting deadlines from detection, so the detection time should be a separate field in the incident log.
- Entities meeting the criteria when the amendment entered into force have 12 months to meet their obligations, and essential entities 24 months for the first audit.
- The management body approves the measures and oversees them, so monitoring and test results should reach management.
Next steps
- Determining whether the organisation meets the criteria for an essential or important entity and checking the application deadline in the minister’s notice.
- Assigning each of the ten measures in Article 21(2) to an owner and a system component.
- Adding a detection-time field and reminders for the 24-hour, 72-hour and one-month deadlines to the incident log.
- Running a backup restore test and recording the result as audit evidence.